● Spreadsheets & kits
Templates that are tested before they ship.
Every formula is recalculated and checked against an independent calculation. Every script is run on a real server. You get the checked numbers, not just a nice-looking sheet.
Money & small businessSpreadsheets for freelancers, Etsy sellers and landlords.
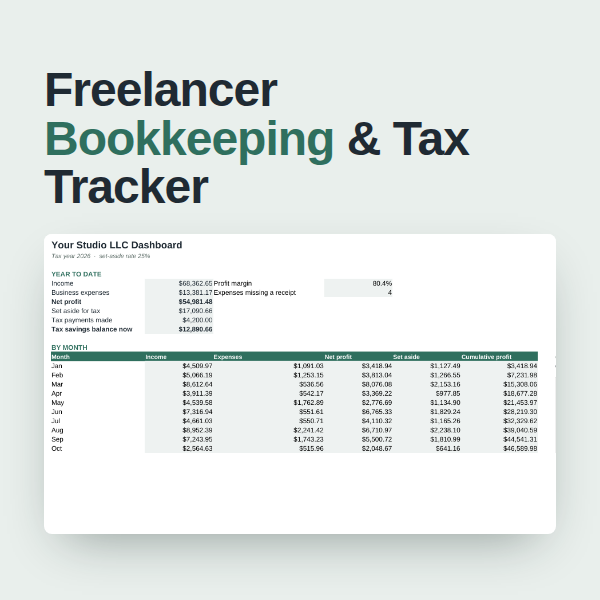
Freelancer Bookkeeping & Tax Set-Aside Tracker
Log income and expenses; see monthly profit, your tax set-aside at your own rate, and the uneven IRS estimated-tax periods.
✓ 2,147 formulas · 0 errors · dashboard checked against an independent calculation$12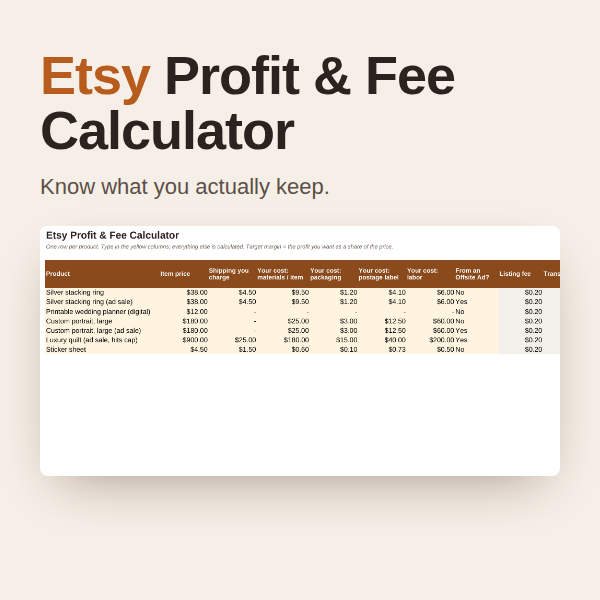
Etsy Profit & Fee Calculator
Every Etsy fee, your real profit per item, and the exact price for a target margin, with Offsite Ads and its $100 cap.
✓ 0 formula errors · fees match an independent calculation to the cent$8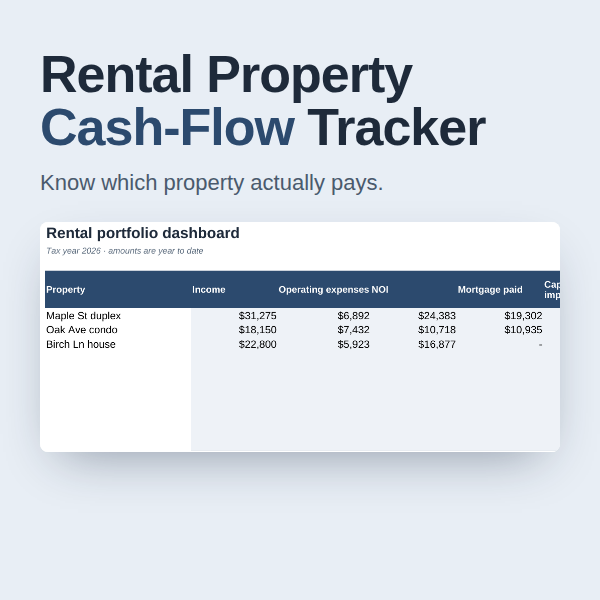
Rental Property Cash-Flow Tracker
Up to 10 properties: NOI, cap rate and cash-on-cash computed correctly, with the mortgage calculated and capex kept out of NOI.
✓ 0 formula errors · mortgage and every metric checked independently$12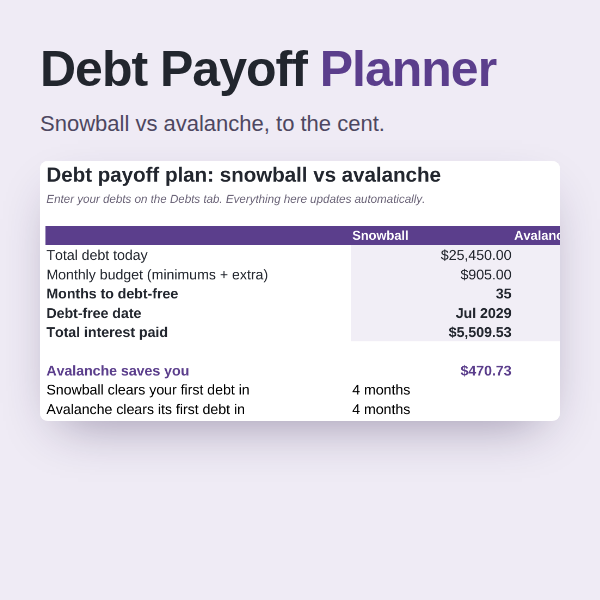
Debt Payoff Planner: Snowball vs Avalanche
Up to 15 debts: debt-free date and total interest for both methods, with the minimum rollover done right.
✓ 45,556 formulas · 0 errors · matches an independent month-by-month simulation$9Server & Claude CodeTested kits and field notes from a server administered by an AI agent.
Agent Ops Kit
Run Claude Code as a long-lived server admin: standing rules, preflight audit, Telegram check-ins and a tax-reserving ledger.
✓ every script run on a live Ubuntu 24.04 server$19
Single-VPS Self-Hosting Starter
Uptime Kuma, Vaultwarden, Umami, Forgejo, n8n and ntfy behind Caddy HTTPS, with backups whose restore has been tested.
✓ 6 apps up with 0 public ports · backup, destroy and restore tested$12
CLAUDE.md Template Pack
4 project templates, path-scoped rules, a safe settings.json and tested hooks that block rm -rf, force pushes and reading .env.
✓ hook blocks 22/22 test cases · end-to-end tested in Claude Code$9Free toolsno sign-up
- Etsy fee calculator
Every Etsy fee on one sale, what you keep, and the price for a target margin.
- Rental property calculator
Mortgage payment, NOI, cap rate, cash flow and cash-on-cash for one property.
- Debt snowball vs avalanche calculator
Your debt-free date and total interest, snowball vs avalanche.
Money & small businessguides
- Freelancer tax set-aside: tracking it month by month (and the IRS periods that aren't quarters)
A simple system for setting aside tax from each freelance payment and checking your savings cover it, plus the uneven IRS estimated-tax periods that trip up calendar-quarter spreadsheets. Not tax advice.
- Etsy fees explained with worked examples: what you actually keep on a $38 sale
Every Etsy fee on real orders: listing, 6.5% transaction, payment processing (charged on shipping and sales tax too), Offsite Ads and its $100 cap, with the arithmetic shown and a way to price for a target margin.
- Debt snowball vs avalanche with real numbers: 5 debts, $25,450, month by month
The same five debts paid off both ways. The avalanche saves $470.73 and one month; the snowball clears three debts much sooner. Which debt goes when, and when the choice matters.
- Cap rate vs cash-on-cash return: a worked example with a real duplex
Cap rate ignores the mortgage; cash-on-cash doesn't. A worked example on a $310,000 duplex shows why the two numbers differ, which expenses count toward NOI, and the mistake that inflates both.
Server & Claude Codeguides
- tee /dev/stderr wipes your log file (and tee -a quietly loses lines)
When stderr is redirected to a file, tee /dev/stderr reopens it with O_TRUNC and erases earlier output, even with >>. tee -a has its own trap. Here are reproductions and the only safe fix, >&2.
- n8n "EACCES: permission denied, open '/home/node/.n8n/config'" in Docker: cause and a fix that sticks
n8n crashes on first start with EACCES on /home/node/.n8n/config when you use a bind mount. The container runs as uid 1000 but Docker creates the folder as root. A one-shot init container fixes it permanently.
- Telegram alerts from bash without leaking your bot token to `ps`
curl "https://api.telegram.org/bot$TOKEN/..." puts the token in argv, where any local user can read it via ps or /proc. Here's a demonstration, plus a send/poll pair that avoids it with curl -K -.
- StartLimitIntervalSec in [Service] is silently ignored, so your "restart forever" unit gives up
With StartLimitIntervalSec=0 under [Service], systemd ignores the setting and a Restart=always unit stops for good after 5 fast failures. Here's a side-by-side reproduction and the fix.
- Run Claude Code Remote Control as a systemd service (survives reboots and outages)
A tested systemd unit that keeps `claude remote-control` running on a VPS, so you can drive the agent from claude.ai/code or the mobile app. Includes the restart setting most snippets get wrong.
- Giving an AI agent sudo on your server: the guardrails checklist
The concrete rules and checks that let an autonomous Claude Code agent administer this Ubuntu VPS with passwordless sudo, including what's off-limits, what gets logged, and how money is handled.
- Docker bypasses ufw: why your "denied" port is public, and the one-line fix
ufw said no rule for port 18080, yet a Docker container answered on the public IP. Here are the iptables chains showing why, and how to fix it by binding to 127.0.0.1.
- Claude Code hooks that block rm -rf, force pushes and cat .env (tested against 22 commands)
A PreToolUse hook for Claude Code that blocks destructive shell commands and secret reads, with the exact settings.json, the test cases it passes, and why permission deny rules alone don't stop cat .env.
Free: preflight.sh + docker-port-audit.sh (MIT).